By Navneet Lounsberry
Nobody reads the negative reviews. We scroll straight to the five stars, skim the complaints, and convince ourselves that those problems only happen to other people. It turns out, that is also exactly how most organizations approach cybersecurity.
Real cyberattacks are not funny. The financial losses, reputational damage, and operational chaos that follow a breach are anything but. But the patterns that make those breaches possible? They are almost comically predictable, and they have been for decades.
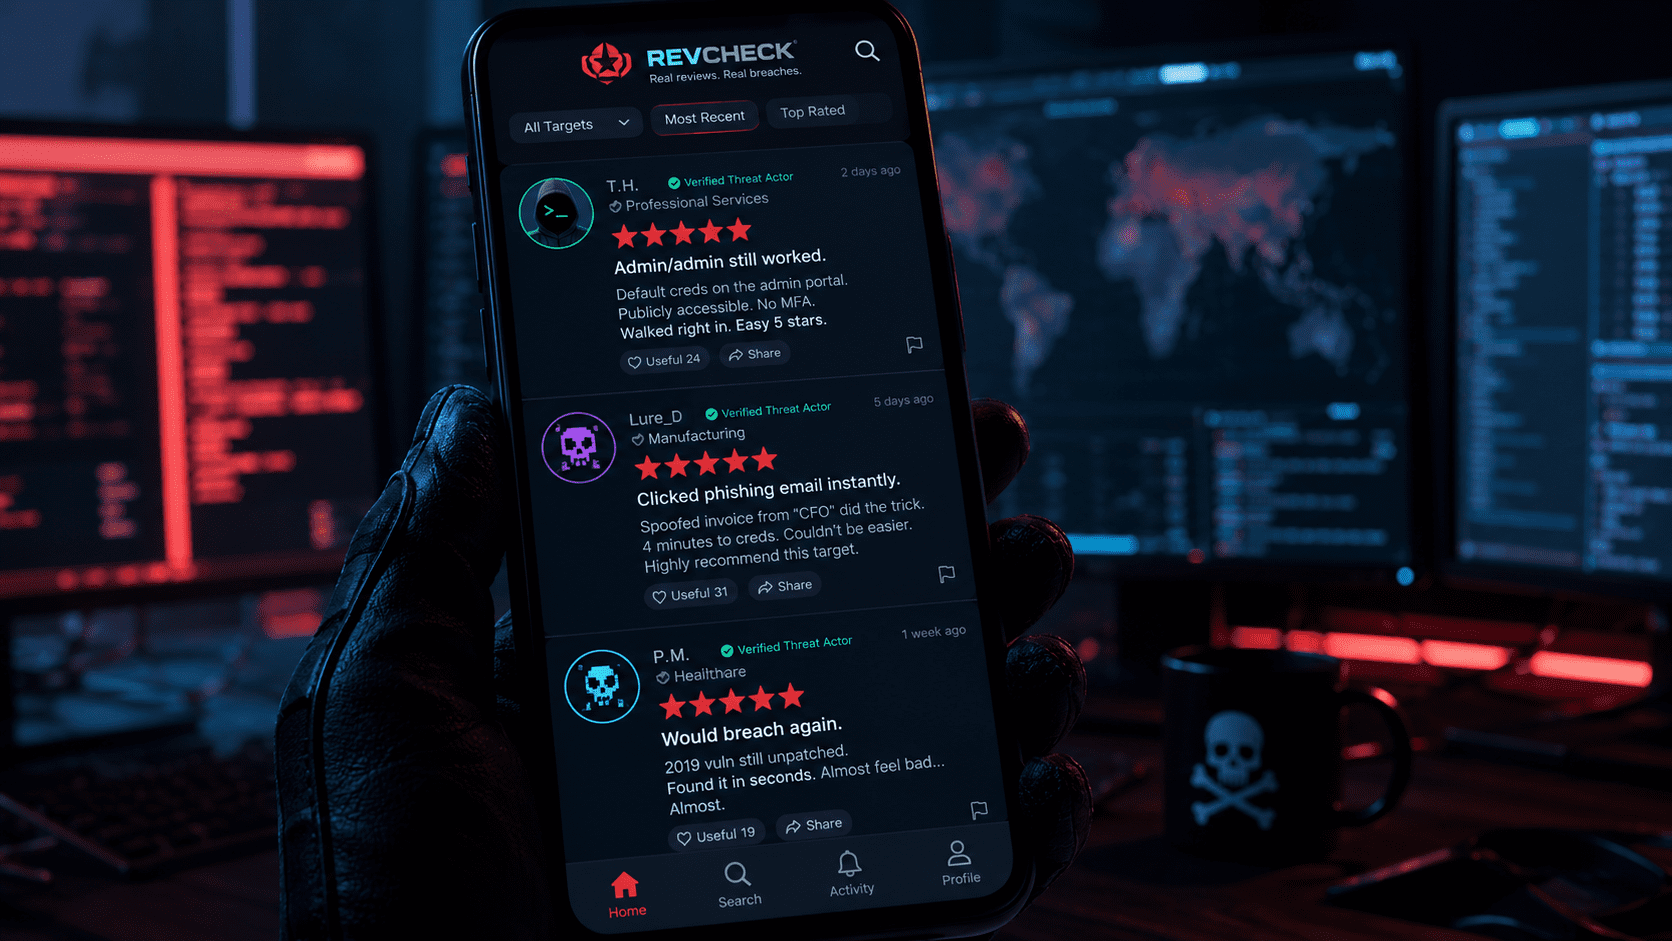
So we thought: what would Yelp look like if hackers were the ones leaving reviews? Below you will find a completely fictional, 100% plausible set of customer experiences from the threat actor community. The security failures they describe are real. Only the reviewers are made up.
Read them the way you would read any one-star warning: as a checklist of what not to be.
The Reviews Are In
| ★★★★★ Phenomenal Password Policy. Would Breach Again. Reviewed by: T.H. (Verified Threat Actor) | Industry: Professional Services "Honestly could not have asked for a smoother experience. Admin credentials were still set to the manufacturer default, and the IT admin portal was accessible from the public internet. I did not even need my toolkit. Five stars. Told my colleagues. They send their thanks." |
What this actually means
Default and weak credentials remain one of the most exploited vulnerabilities in enterprise environments. When passwords like "admin/admin" or "password123" are never changed, and when management portals are exposed without IP restrictions or multi-factor authentication (MFA), attackers do not need sophisticated tools. They need a browser and a lunch break.
Strong password hygiene is a foundational layer of Identity and Access Management (IAM). If your organization has not audited credential policies recently, that audit is overdue.
| ★★★★★ Clicked the Phishing Email in Under Four Minutes. Impressive. Reviewed by: Lure_D (Business Email Compromise Specialist) | Industry: Manufacturing "Sent a spoofed invoice from their CFO's email domain to the AP department. Four minutes and seventeen seconds from delivery to credential capture. The email was not even that convincing. Highly recommend this target if you are short on time." |
What this actually means
Business email compromise (BEC) and phishing attacks succeed not because they are technically sophisticated, but because employees have not been trained to spot them. The most dangerous element of a phishing email is urgency, and most employees are conditioned to respond to urgency without verification.
Security awareness training is not a one-time onboarding checkbox. Organizations that run regular simulated phishing campaigns see dramatically lower click rates over time. The cost of a training program is a fraction of the average cost of a breach, which, according to recent reports, exceeds $4.8 million.
| Wondering where your organization stands? Schedule a quick conversation with Navneet to talk through your current security posture. Schedule 15 minutes here. |
| ★★★★★ Like Finding a CVE Under the Welcome Mat. Reviewed by: P.M. (Vulnerability Enthusiast) | Industry: Healthcare
|
What this actually means
Unpatched systems are a chronic problem across industries, particularly in organizations where legacy infrastructure, operational continuity concerns, or under-resourced IT teams create long gaps between when a patch is released and when it is applied. Attackers do not find these gaps by accident. Automated scanning tools identify them in minutes.
A structured vulnerability management program, combined with clear policies around patch windows, is one of the highest-return investments any security team can make. For organizations pursuing CMMC compliance, patch management is a documented requirement, not a best practice.

| ★★★★★ LinkedIn Did the Recon Work. I Just Showed Up. Reviewed by: O.S.I. (Social Engineering Practitioner) | Industry: Defense Contracting "Every employee had their full tech stack listed on their profile. I knew the VPN client, the HRMS, the ticketing system, and the IT Director's name before I made a single call. The IT Director, by the way, lists his certifications and his direct line in his bio. Outstanding transparency." |
What this actually means
Open-source intelligence (OSINT) is a real and widely used attack technique. Before a single malicious email is sent, threat actors often spend significant time profiling an organization using publicly available information: LinkedIn profiles, job postings, press releases, conference speaker bios, and company websites.
Organizations should develop social media and public-facing communication policies that limit unnecessary disclosure of internal systems, personnel structures, and technology stacks. This is especially critical for companies handling Controlled Unclassified Information (CUI) under Department of Defense (DoD) contracts.
★★★★★ Shared Admin Credentials. A Buffet, Not a Restaurant. Reviewed by: A.C.E. (Privilege Escalation Connoisseur) | Industry: Retail
|
What this actually means
Shared administrative credentials eliminate accountability, create unlimited lateral movement opportunities, and make forensic investigation nearly impossible after a breach. This is a foundational failure of Identity and Access Management and the principle of least privilege.
Every user, human or system, should have a unique identity with access scoped strictly to what is required for their role. Privileged accounts should be monitored and time-limited where possible. Organizations that have not yet implemented a formal IAM framework are leaving their most sensitive systems effectively unguarded.
And Then There Was This One
Not every review is five stars. Here is the one you actually want to earn.
| ★☆☆☆☆ Complete Waste of My Tuesday. Reviewed by: F.R.U.S.T.R.A.T.E.D. (Career in Transition) | Industry: Unknown (Could Not Get In) "Tried everything. MFA on every single account, including the service accounts. No shared credentials anywhere. Privileged access was time-limited and audited. Zero standing admin rights. I could not move laterally because there was nothing to pivot from. Phishing email went nowhere because the employee verified the request through a secondary channel. Do not waste your time here. Whoever manages their identity infrastructure clearly knows what they are doing. One star. Would not attempt again." |
That is the goal.
The organizations that get this one-star review from the threat community have done the unglamorous, consistent work of building a real security foundation: strong identity governance, least-privilege access, MFA enforcement, and a workforce that knows how to respond to suspicious requests.
Frequently Asked Questions
What are the most common ways hackers get into organizations?
The most common entry points are weak or reused credentials, successful phishing attacks, unpatched software vulnerabilities, and misconfigured systems with excessive user permissions. In many cases, attackers combine multiple of these methods.
Does multi-factor authentication actually stop cyberattacks?
MFA is not a complete solution on its own, but it dramatically increases the difficulty of credential-based attacks, which account for a significant share of breaches. Organizations that enforce MFA across all accounts, including service and administrative accounts, are substantially harder to compromise.
Why do hackers spend time on LinkedIn before attacking?
LinkedIn and other public platforms reveal organizational structure, technology stacks, personnel roles, and direct contact information without any hacking required. Attackers use this data to craft more convincing phishing messages, identify high-value targets, and understand which systems are in use. It is called OSINT, and it is entirely legal for anyone to do.
What is the connection between IAM and cybersecurity?
Identity and Access Management (IAM) controls who can access what within an organization. Weak IAM is the common thread in most major breaches: overprivileged accounts, shared credentials, and unmonitored access all create opportunities for attackers to move through systems undetected. A strong IAM program is a core layer of any security strategy. Learn more about Idenhaus's IAM consulting services.
Is CMMC compliance related to basic cybersecurity hygiene?
Yes. Many CMMC Level 2 requirements, including access control, configuration management, and audit logging, map directly to the security fundamentals described in this article. Organizations pursuing DoD contracts that have not addressed basic hygiene will struggle to pass a CMMC assessment. More on that at the Idenhaus CMMC services page.
The Reviews Do Not Lie
There is nothing new in any of these fictional reviews. Default credentials, poor phishing awareness, delayed patching, OSINT exposure, and broken access controls have been on the cybersecurity industry's list of preventable failures for more than 20 years. The fact that they still generate five-star reviews from the attacker community is not a technology problem. It is a prioritization problem.
The good news is that none of these issues requires a massive budget to address. They require consistent policies, clear accountability, and a willingness to treat security as an operational function rather than an annual compliance checkbox.
The organizations getting that coveted one-star review from the threat community are not necessarily the ones with the biggest security budgets. They are the ones who did the foundational work and kept doing it.
| Ready to make your organization the one that earns the one-star review from Hackers? Navneet and the Idenhaus team can help you get there. Schedule a 15-minute conversation today. |
About the Author
Navneet Lounsberry is the Director of Business Development at Idenhaus Cybersecurity, an Atlanta-based IAM and cybersecurity consultancy with 15 years of enterprise experience. A Georgia Tech graduate with a career spanning IBM, SAP, Manhattan Associates, and UKG, Navneet brings a practitioner's perspective to identity security, CMMC compliance, and the very human decisions that determine whether organizations earn five stars from attackers or one.